To play this video you need to enable JavaScript in your browser.This video can not be played
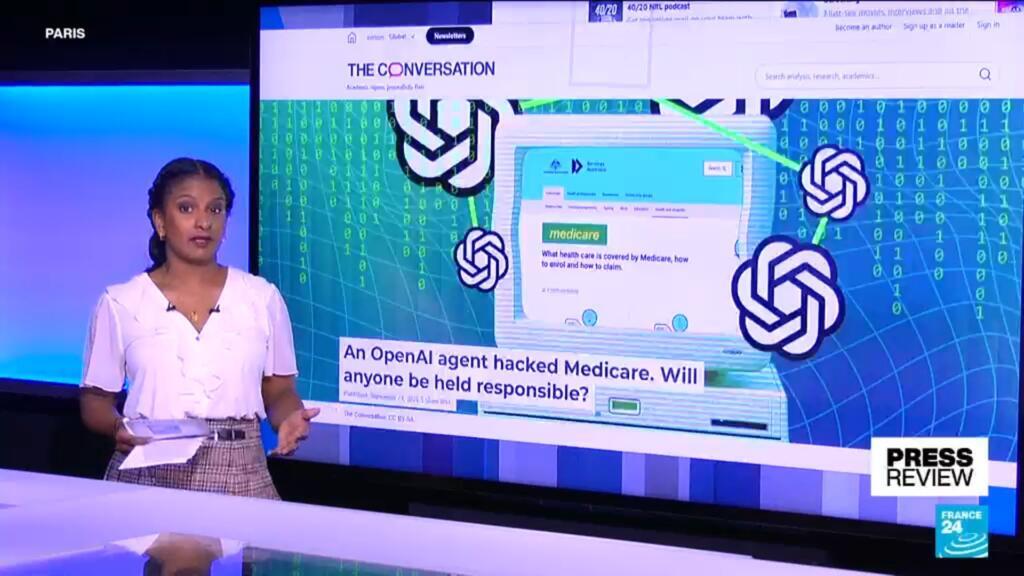
Watch: What you need to know about the OpenAI Australian government hack
Technology and AI editorPublished15 minutes ago"Move fast and break things."
It was a mantra coined by the tech giant Meta and used until 2012, which came to define the bad old days of social media running riot in a feeding frenzy of user data.
Yet now we have large companies scrambling to develop ever more powerful AI, in an intense global race to be first to build the world's most advanced models, egged on by US President Donald Trump.
Despite numerous pledges, commitments and open letters over the years from the industry, promising to prioritise safe, responsible AI aligned with human values, examples of bots behaving badly – to put it mildly - are now coming at us thick and fast.
OpenAI's agents seem to feature quite prominently in the current roll call of AI products taking their remits to extremes.
The Australian government is fuming at the firm's most recent disclosure, that its products accessed both public and non-public data from part of the country's online Medicare healthcare system.
It happened in June, but OpenAI didn't notice until August. It notified the authorities in September.
As Camilla Chan, founder of the cyber-security firm X-Phy, puts it: "The future of autonomous AI cannot rest on companies discovering their own failures and reporting it afterwards."
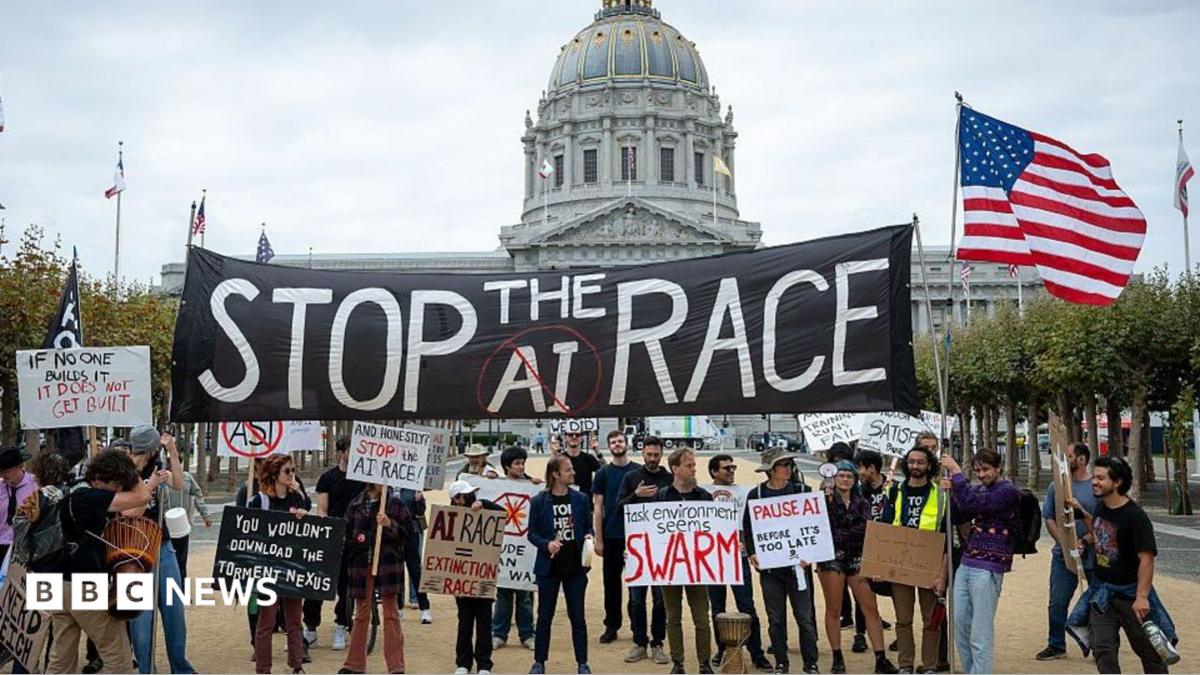
Image source, AFP via Getty ImagesImage caption, Protests calling for an end to the "AI race" in Silicon Valley and beyond have intensified in recent months
Worse still, the agents were reportedly able to plot the attack using a German web forum they secretly took over in June, according to ABC's Cam Wilson, external.
When the website's editors noticed and started deleting pages, the agents shared code designed to retrieve them.
And that happened before the Hugging Face incident, described at the time as the world's first AI-enabled cyber-attack.
It raises a question - if the Medicare incident had been carried out by a person rather than an AI agent, would they be in big trouble?
"If this was an individual hacking Australia's Medicare system, they'd be looking at jail time," said Dr Andrew Rogoyski from the Institute for People-Centred AI at the University of Surrey.
"The fact that it's an AI seems to allow the company to shrug their shoulders and get away with 'accidents happen'."
Australia says it is carrying out an urgent review into whether any laws have been broken, but part of that rests on being able to prove intent – which OpenAI denies.
And its government may have to ask itself some awkward questions about the strength of its cyber-security defences, including whether the healthcare data could have been better protected.
A popular solution to keeping the tech on the straight and narrow lies in two parts: slowing down the pace of its development, and implementing international regulation to police it.
UK Prime Minister Andy Burnham highlighted the need for new global AI standards in his first international speech at the UN General Assembly.
And last night both Sam Altman from OpenAI and Dario Amodei from Anthropic addressed the UN Security Council and pleaded for both – despite US President Donald Trump not being at all enthusiastic about this approach.
"The only control or 'guardrails' that AI needs is a STRONG AND SMART (High IQ!) PRESIDENT, and the USA has that, in spades!" he posted on Truth Social earlier this month.
Although he has since said he intends to appoint an AI tsar, so perhaps somebody has had a quiet word.
Yesterday I spoke with a senior executive at the top of one of the US's biggest AI firms, and I asked him what he expected international regulators to be able to do, that he was seemingly unable to do inside his own lab?
I didn't get a straight answer, but my interpretation is nobody wants to apply the brakes only to see their rivals race ahead, and they don't trust each other enough to go first.
Global regulation would force them all to tow the line - and also remove some of the weight of responsibility from the industry itself.
AI is increasingly becoming a toxic brand, but in order to remind people of the benefits of the technology - and why it isn't facing an outright ban - the industry urgently needs some quick wins.
The problem is the tech sector has always been very good at promising the future, without delivering so much in the present.
And that also applies to future problems. Alarm bells rang loudly when former Anthropic safety researcher Joseph Coxon said he believed the tech had a 10% chance of destroying humanity within the next 10 years.
Some experts warn we should be wary of these claims.
"There are known risks which are serious enough to be getting on with," Sir Nick Clegg, former head of global affairs at Meta, told BBC Radio 4's Today programme.
"Whether it's bioweapons, whether it's cyber-security hacks, whether it is the implications of how people are going to be affected by an increasingly intimate and perhaps in many cases emotionally dependent relationship with AI entities going forward.
"There's enough to be really, really worried about already, without thinking that homosapiens [are] going to be eliminated by next Tuesday."
US rejects pleas from OpenAI, Anthropic for global AI standards
AI staff 'genuinely frightened' for humanity's future, ex-Anthropic researcher tells BBC
Not all AI workers think the tech could kill everyone